Counterparty Verification
Why Counterparty Verification Matters: Shielding Your Business from Risk
Counterparty verification checks a partner's identity, legal standing, sanctions exposure and financial condition before any deal or relationship moves forward. The process relies on KYC document checks, OFAC and FATF-aligned screening, and risk-based monitoring — work that reduces exposure to money laundering, fraud and regulatory penalties.
OS Olivia Shaw 10 min read
What Counterparty Verification Means
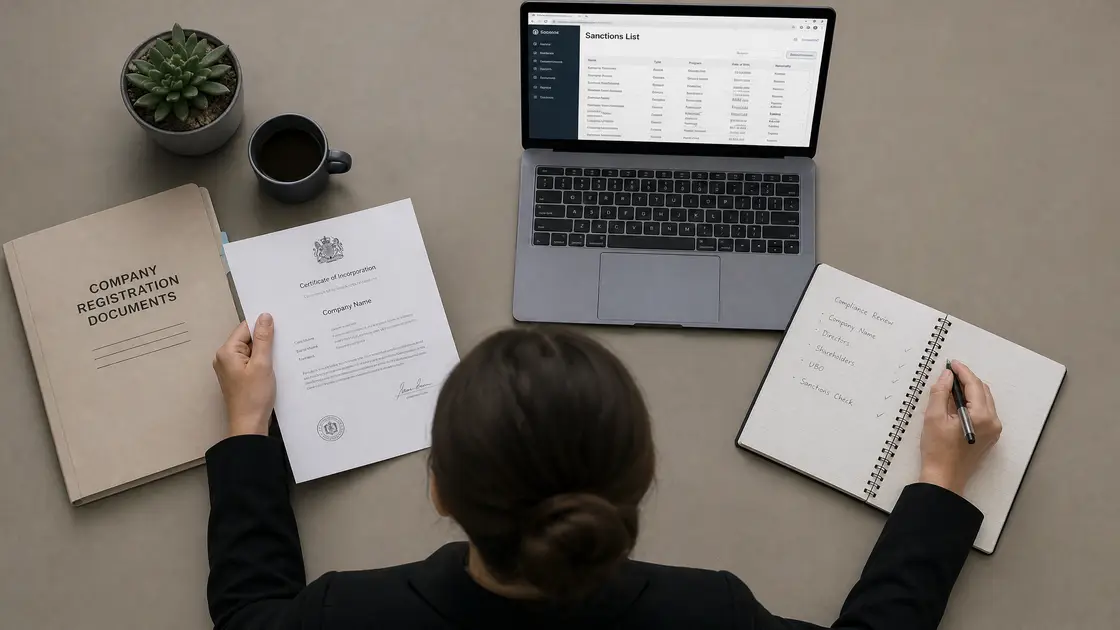
Counterparty verification confirms who a prospective partner actually is, whether it legally exists, and what risk it carries, all before any deal goes ahead. Identity, registration status and risk profile are three separate questions; a solid answer to one says nothing about the other two.
This differs from a generic background check in one key respect: verification attaches itself to a live transaction or relationship, and its depth scales with the money, goods and legal exposure at stake. A single cross-border purchase and a supplier invoiced monthly for years both require it, though the second calls for periodic refreshing rather than a one-off sign-off.
What Information to Collect for a Background Check
A background check on a counterparty is only as reliable as the records feeding it. Four categories of information do most of the work, and none can substitute for another.
Gaps often say as much as findings do. A company unable to produce ownership documents, or one whose filings stop abruptly years ago, has already shown something about its risk profile.
- Legal registration details: company number, incorporation date, registered address, current status and the chain of beneficial ownership behind the trading name.
- Sanctions and watchlist status for the entity, its parent companies and the individuals who ultimately control it.
- Financial statements and credit history, including filed accounts, payment behaviour and any indication of insolvency proceedings.
- Litigation and regulatory enforcement history, covering court judgments, licence withdrawals and penalties imposed by financial or trade regulators.
KYC Steps for Verifying a Business Counterparty
KYC for a business counterparty tends to follow a fixed sequence, and a skipped stage usually goes unnoticed until something breaks. Order matters here, since each step narrows what the next one needs to examine.
The sequence below mirrors the search, filter and screening workflow this site uses when testing company-database providers for review.
- Collect identity and ownership documents directly from the counterparty: incorporation certificate, directors' identification and a declaration of beneficial owners above the relevant threshold.
- Verify those documents against independent sources, such as the national company register and recent statutory filings.
- Screen the entity and its controllers against sanctions lists and politically exposed person databases, including name variants and transliterations.
- Assign a risk tier — low, elevated or high — based on jurisdiction, ownership opacity, sector and screening results.
- Set up ongoing monitoring proportionate to that tier, so a later change in ownership or sanctions status surfaces without a fresh manual review.
- Document every finding, source and decision in a form an auditor or regulator can follow months later.
Counterparty Risk Assessment vs Traditional Due Diligence
The two terms get used interchangeably, but they describe different habits of work. Traditional due diligence delivers a verdict tied to a single date; counterparty risk assessment keeps that verdict alive, updating it as the evidence shifts.
Neither approach makes the other obsolete. What decides between them is usually the size and duration of the relationship in question.
| Dimension | Counterparty risk assessment | Traditional due diligence |
|---|---|---|
| Scope | Continuous monitoring with alerts when status changes | Point-in-time check completed before signature |
| Data sources | Registry feeds, sanctions lists, credit and payment data refreshed on a schedule | Documents supplied by the counterparty plus commissioned reports and interviews |
| Automation | High: screening, matching and alerting are largely system-driven | Low to moderate: analyst-led review with manual document handling |
| Typical use case | A recurring supplier, distributor or payment partner | A one-time acquisition, tender or large single transaction |
OFAC and Sanctions Screening in the Verification Process
Sanctions screening is the point where a commercially attractive partner can turn legally untouchable overnight. The Office of Foreign Assets Control administers US sanctions programmes and publishes the lists that names, vessels, addresses and wallet identifiers get matched against.
Screening sits between document collection and risk tiering. Identity has to be established before a name can be meaningfully screened, and the result of that screening then decides the tier.
- OFAC designates sanctioned individuals, entities, vessels and digital-asset addresses, and its consolidated listings serve as the reference point for most screening tools.
- Screening covers the counterparty itself, its parents and subsidiaries, and its beneficial owners, since ownership thresholds can pull an unlisted company into scope.
- The FATF Recommendations supply the international framework underpinning national sanctions and AML/CFT regimes, which explains why screening logic looks broadly similar across jurisdictions.
- Dealing with a sanctioned party exposes a business to asset freezes, civil and criminal penalties, and lost correspondent banking access — regardless of whether the breach was intentional.
Detecting Money Laundering and Terrorist-Financing Risks
Laundering typologies usually surface first in counterparty analysis, because the shape of a relationship reveals more than any single payment ever could. AML/CFT controls work by connecting what verification learned about a partner with what transaction monitoring later observes about its behaviour.
Terrorist financing calls for the same screening machinery even when the sums involved are small, since the risk sits in the destination of the money rather than its size.
- Payment instructions routed through third countries or unrelated entities, or requests to split invoices below reporting thresholds.
- Ownership traced to shell companies in opaque jurisdictions, with nominee directors and no verifiable operating premises.
- Transaction volumes that bear no relation to the counterparty's filed turnover, headcount or stated line of business.
- Sudden changes in banking details, beneficial owners or trading patterns shortly after onboarding.
Laundering rarely hides in a single payment; it hides in the structure of a relationship nobody thought worth re-examining after onboarding.
Third-Party Due Diligence in the Shipping Industry
Shipping depends on intermediaries at every stage. A single voyage might involve a chartering broker, a local agent, a freight forwarder and a vessel owner registered somewhere none of them actually operate, which is why third-party due diligence carries as much weight here as direct contracting does elsewhere.
Picture a forwarder brought on for a routine route, screened once at onboarding and never checked again. The vessel it later sub-charters turns out to be beneficially owned by a sanctioned party, and the cargo gets detained — the breach slips in through a relationship nobody re-examined. Sector-specific checks help here: vessel ownership and flag history, port-state control records, and AIS gaps hinting at concealed calls.
On-Chain Counterparty Verification in Cryptocurrency Transactions
On-chain verification establishes who a counterparty is by tracing wallet addresses and transaction history instead of reading documents. Public ledgers record every transfer, so a wallet's counterparties, age and exposure to flagged services can be reconstructed straight from the chain.
In crypto deals this partially replaces traditional identity evidence: the address becomes the verifiable credential, and behaviour across the ledger becomes the reputational record. Supporting checks still matter — smart-contract audits confirm whether the code governing funds does what its documentation claims, while wallet screening matches addresses against sanctions designations and known mixer or darknet clusters before any transfer is authorised.
Compliance Frameworks Shaping Counterparty Verification
Verification policy rarely starts from a blank page. It operates inside a layered framework, with international standards at the top and national supervisors translating them into enforceable obligations further down.
Because those layers move at different speeds, a policy written once and filed away drifts out of step within a few cycles.
- The FATF Recommendations set the baseline international standard for AML/CFT, establishing expectations on customer due diligence, beneficial ownership and risk-based controls.
- Regional and national regulators periodically revise their AML/CFT rules, adjusting thresholds, record-keeping duties and the scope of obliged entities.
- Sanctions programmes change far more often than legislation does, which makes list refresh frequency a compliance matter rather than a technical detail.
- Most frameworks require a documented verification policy to be reviewed periodically and after any material change in risk, with evidence that the review actually happened.
Consequences of Inadequate Counterparty Verification
Under-investing in verification rarely sends an immediate warning. The cost shows up later, typically through a regulator, a bank, or a contract that simply can't be performed.
Risk management treats these outcomes as connected: one triggered penalty tends to pull the others along behind it.
- Financial penalties and regulatory fines, often calculated against transaction value rather than the profit actually earned on the deal.
- Reputational damage that follows a company into tenders, insurance renewals and investor conversations.
- Loss of banking relationships, as correspondent banks and payment providers choose to de-risk rather than investigate.
- Operational disruption from frozen transactions, detained goods and contracts cancelled once a partner's real risk profile comes to light.
FAQ: Financial Health Tools, Standards and Ongoing Checks
Three questions keep coming up once a verification policy moves from principle into practice: what tools to use, how far to go, and how often to repeat the work.
What tools help assess a counterparty's financial health?
Credit reports, filed financial statements, payment-history trackers and insolvency registers cover most of the ground. Company databases that aggregate registry filings help spot late accounts or status changes, while trade-credit insurers and payment-behaviour data show how a counterparty actually settles invoices rather than how it describes itself.
How do best practices differ from formal industry standards?
Standards mark a floor: the minimum documents, thresholds and record-keeping a regulator will accept. Best practice goes further — screening beneficial owners rather than just the contracting entity, monitoring continuously rather than annually, and documenting the reasoning behind each risk tier so decisions hold up years later.
Is counterparty verification a one-time task or an ongoing obligation?
It stays ongoing for as long as the relationship lasts. Ownership changes, sanctions designations and financial deterioration all happen after onboarding, so a check done at signature says nothing about the position six months on. Risk-based monitoring, with refresh intervals tied to the assigned tier, is the practical answer.
Counterparty verification brings together identity confirmation, sanctions screening and financial-health review, establishing a partner's legitimacy before money or goods change hands. It leans on KYC procedures, OFAC and FATF-aligned screening, and monitoring that continues well past onboarding rather than stopping at a single checkpoint. Skipping it leaves a company exposed to money-laundering liability, sanctions penalties, lost banking access and agreements that unravel once a partner's real risk profile comes out.
On the same topic
Topics
- #Counterparty Verification
- #Business Risk
About the author
Editor-in-chief, 6 years in company research, degree in journalism
Olivia Shaw has spent six years examining how company databases present their information, testing what they claim against what can actually be verified. At DataBuss, she checks facts and figures before any rating is published, tracing numbers back to their original source whenever possible. Her background in journalism shaped a habit of asking where a claim comes from, rather than accepting it at face value. Readers can expect her reviews to lean on verifiable detail instead of marketing language.
Writes about: fact-checking and data verification
Articles by this authorRead next
How to Use Company Databases for B2B Sales: A Step-by-Step Guide
A B2B leads database pays for itself only when it powers a real process: verified contact and firmographic records, scored and segmented inside a CRM, then…